What happened
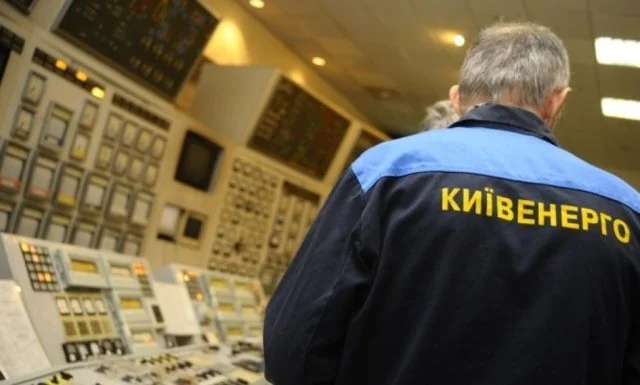
On 23 December 2015, three Ukrainian regional electricity distribution companies experienced coordinated outages after what a US government alert describes as illegal entry into their computer and supervisory control systems; roughly 225,000 customers lost power for several hours. A joint report by the SANS Industrial Control Systems team and the Electricity Information Sharing and Analysis Center, published on 18 March 2016, found the attackers had used spear-phishing emails to gain an initial foothold, harvested credentials, then used remote-access tools and virtual private network connections to reach supervisory control software and directly issue commands opening circuit breakers, before deploying destructive disk-wiping malware to delay recovery.
Confidence and limits
The joint report rates its own credibility as confirmed, citing malware samples, interviews with operators present during the incident, and independent corroboration from multiple companies and the US government's own alert, which itself cites direct interviews with staff at six Ukrainian organizations. Both documents are unusual for stating plainly what they do not establish: the joint report says outright that it does not focus on attribution of the attack, and it treats the malware found, BlackEnergy 3 and a disk-wiping tool, as enabling components rather than as proof by themselves of who was responsible or the sole cause of the outage.
Why it mattered
This was the first publicly documented case of a cyberattack causing an electricity outage, and the joint report's most cited operational finding is how the outage ended: engineers restored service by traveling to substations and operating breakers manually, because the attackers had also disabled remote recovery options by overwriting device firmware and wiping operator workstations. The report frames the attackers' destructive final steps, which it describes as burning the bridges, as a deliberate effort to slow restoration rather than to cause the outage itself, which was achieved through direct manipulation of the control software.
Defensive takeaway
Review whether your organization's manual-operations fallback for critical systems has actually been rehearsed by the staff who would need to execute it, and whether remote-access paths into control networks require multi-factor authentication.
- Could your control-network operators switch to manual operation today if supervisory software could no longer be trusted?
- Do remote-access and VPN connections into your operational technology network require two-factor authentication?
- Would your organization detect malicious firmware being pushed to field devices before it was executed, not just after?
The joint report's discipline about attribution is itself part of what it establishes: it demonstrates that an incident can be documented in operational and technical detail, sufficient to draw defensive lessons, without the authors claiming to know who was behind it, a distinction worth preserving whenever a later, less careful account asserts a confident answer this original analysis did not.
Confirm your organization has a tested, rehearsed procedure for operating critical systems manually if supervisory control software becomes untrustworthy, not just a written plan that has never been exercised.
A joint SANS Industrial Control Systems and E-ISAC analysis, corroborated by a US government alert citing direct interviews with affected utility staff, establishes the sequence of the attack; the joint analysis explicitly states it does not address attribution, and this article does not name any attacker or government as responsible.
Sources & reading trail
US government alert, based on interviews with affected utility staff, confirming the coordinated attack, credential theft, and use of destructive malware.
government-primary · Source published: 25 February 2016 · Retrieved: 16 September 2026
Joint SANS/E-ISAC technical analysis of the attack sequence, manual restoration, and explicit decision not to address attribution.
project-primary · Source published: 18 March 2016 · Retrieved: 16 September 2026
Official records establish the facts; confidence labels and defensive takeaways are Patch & Proof editorial analysis. This retrospective draft does not imply the site published on the event date.