patch&proof.
The briefing ↗
THE INDEPENDENT SECURITY RESEARCH JOURNAL

Independent cybersecurity research

Follow the
evidence.
Strengthen
the defense.

Understand what happened.
Know what matters. Build what comes next.

RESEARCH / CONTEXT / ACTION↓
Historical incident atlasDrag to explore
+
Europe in focusCountry reference locations · 2000–2024
Affected-country records
DOCUMENTED HISTORY. NOT LIVE ATTACKS.Open the atlas ↗
100Source-led historical case files
3,152Mapped historical incidents
31Research chapters & field guides
166Affected countries & territories
THE VISUAL RECORDAll 117 source plates ↗

01 / THE EVIDENCE DESK

Real incidents. Lasting lessons.

All case files ↗

02 / INTERACTIVE CHRONOLOGY

Different decades.
Familiar failure modes.

Move through the archive. Connect the incidents to the standards, disclosures and defensive shifts that followed.

Explore the timeline ↗

03 / THE SOURCE MATERIAL

Look closer.

Enter the evidence room ↗
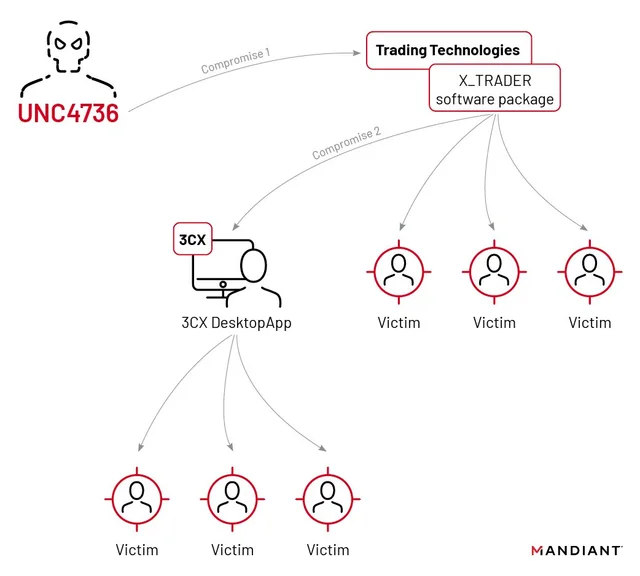
Original figure from Mandiant’s June 2024 investigation; it reflects the report’s investigative scope. Image: Mandiant / Google Cloud ↗Source image · credit and context below
Original research / Mandiant

A diagram is useful.
Its context is essential.

See how investigators reconstructed the credential trail in the Snowflake customer campaign. Read the boundaries of the claim, not just the headline.

Open the case file ↗

04 / PRACTICE THE RESPONSE

Reading is the start.
Make the next decision.

Build a baseline, work through an incident scenario, or navigate the six NIST CSF functions.

Open your workbench ↗

05 / VULNERABILITY DESK

Known exploitation. Clear next action.

Search the catalog ↗

The Patch & Proof briefing

A little less noise.
A lot more context.

Source-led security reading, delivered with perspective. One publication. Your choice to subscribe.

Explore the briefing ↗Your privacy →
Search the evidence
Source image / inspection view

View original source ↗Source credits and usage context remain attached. Check original terms before reusing an image.